Skip to content

One description of your service. The right resources on each cloud.

Each environment's settings live in SKE and become compute, data, queues and networking in your own account.

storefront / production

Runtime    Laravel
Network    aws-maingcp-main
Region     us-east-1us-central1
Memory     1024 MB
Scheduler  On
Queues     default, timeout 60 s
Domains    shop.example.com

Provisions in your account

ComputeCompute
LambdaCloud Run
ImagesImages
ECRArtifact Registry
QueuesQueues
SQSCloud Tasks
ScheduleSchedule
EventBridgeCloud Scheduler
LogsLogs
CloudWatchCloud Logging
StackNetwork
CloudFormationVPC connector

Google Cloud is in early access.

A workflow engineers can script.

Deploys, rollbacks and secrets run from one CLI, so pipelines and people follow the same process.

curl -fsSL https://get.ske.io/install.sh | sh
  1. Connect

    Sign in, then link an AWS role or a GCP service account from the dashboard.

    ske login
  2. Link

    Ties the repository to a project and environment. Memory, queues, hooks and domains are environment settings, so the repository needs no config file.

    ske link
  3. Configure

    Values are prompted, stored in your account and injected at startup. Never committed.

    ske secret set STRIPE_SECRET --env production
  4. Ship

    Builds the image, pushes it to your registry, runs deploy hooks and switches traffic.

    ske deploy --env production
  5. Undo

    Points traffic back at the previous release. No rebuild.

    ske rollback

Everything included, grouped the way you evaluate it.

Governance and access

Control who can see, change and ship each part of your estate, and prove it later.
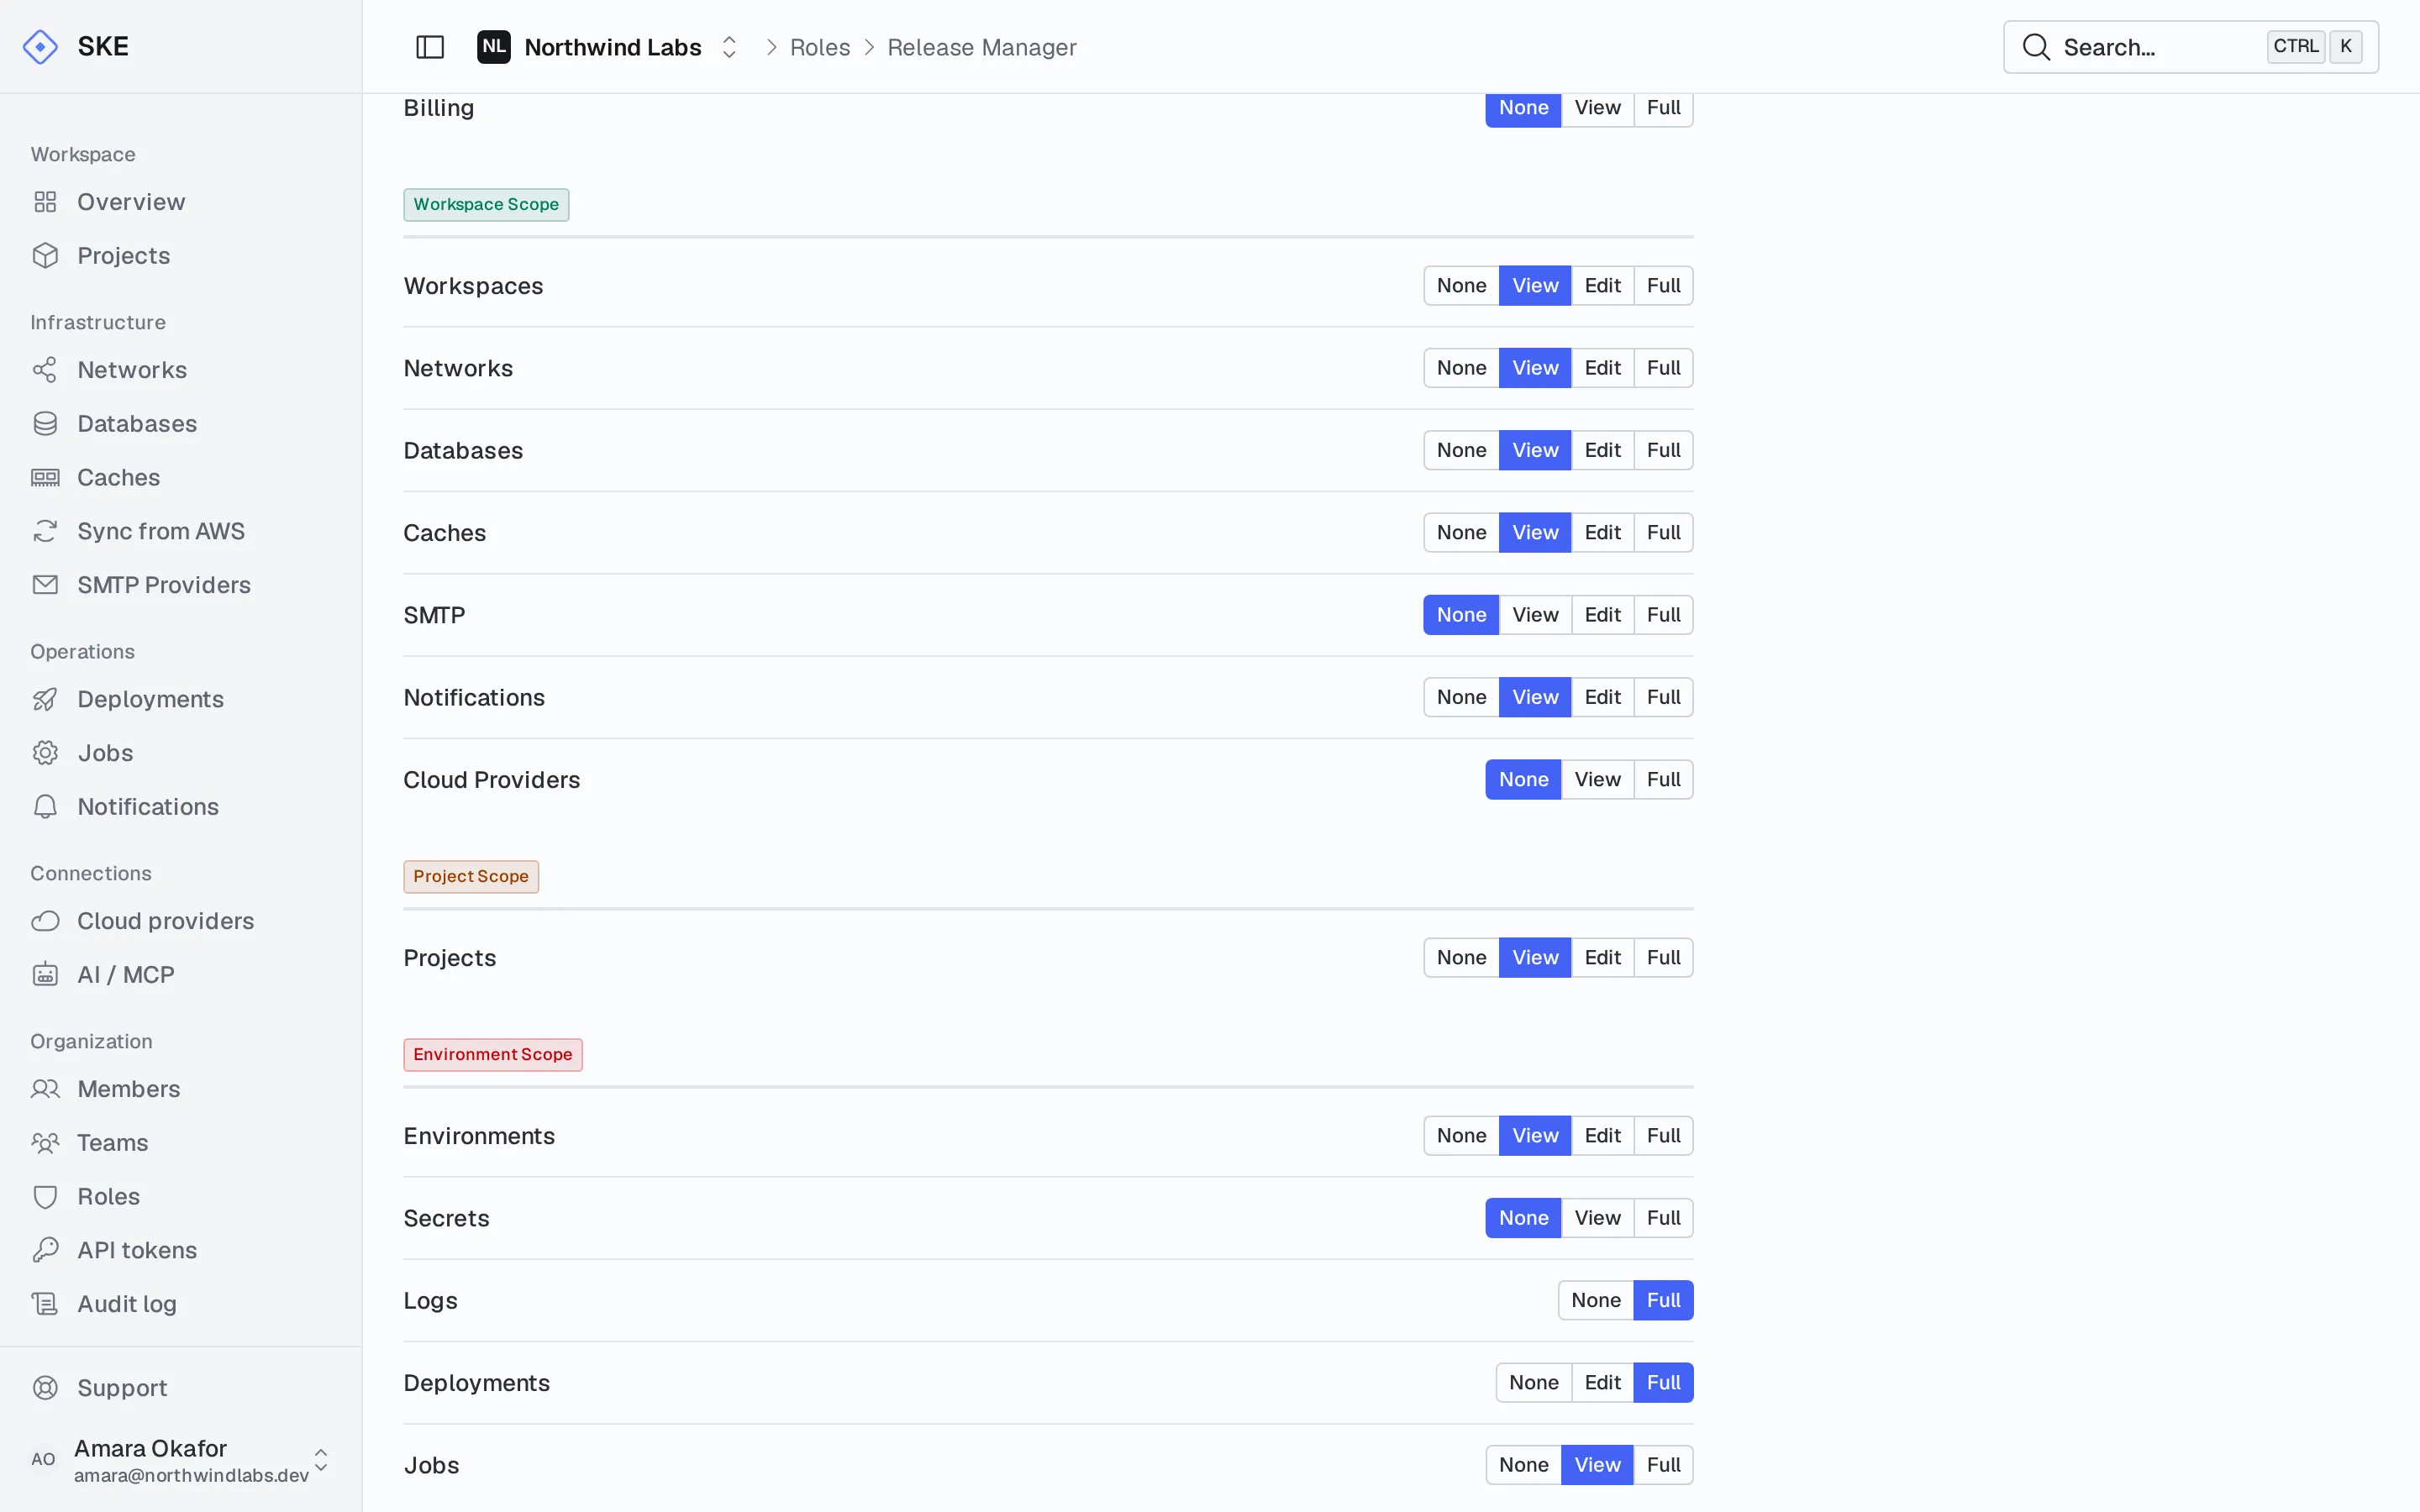
The SKE role editor for a custom Release Manager role, with an access level of None, View, Edit or Full chosen for each area.
Organizations and workspaces
Group projects and cloud accounts by team, business unit or client, each with its own access.
Roles at every level
Grant roles on the organization, a workspace, a project or a single environment. Teams inherit their roles.
Custom roles
Compose roles from granular permissions, from viewing logs to deploying to protected environments.
Protected environments
Production deploys require a dedicated permission and an explicit confirmation.
Scoped API tokens
Tokens are limited to chosen projects or environments, cannot exceed their creator, and expire within a year.
Audit log
Every change to deployments, environments, roles and infrastructure, with before and after values.
Deployment

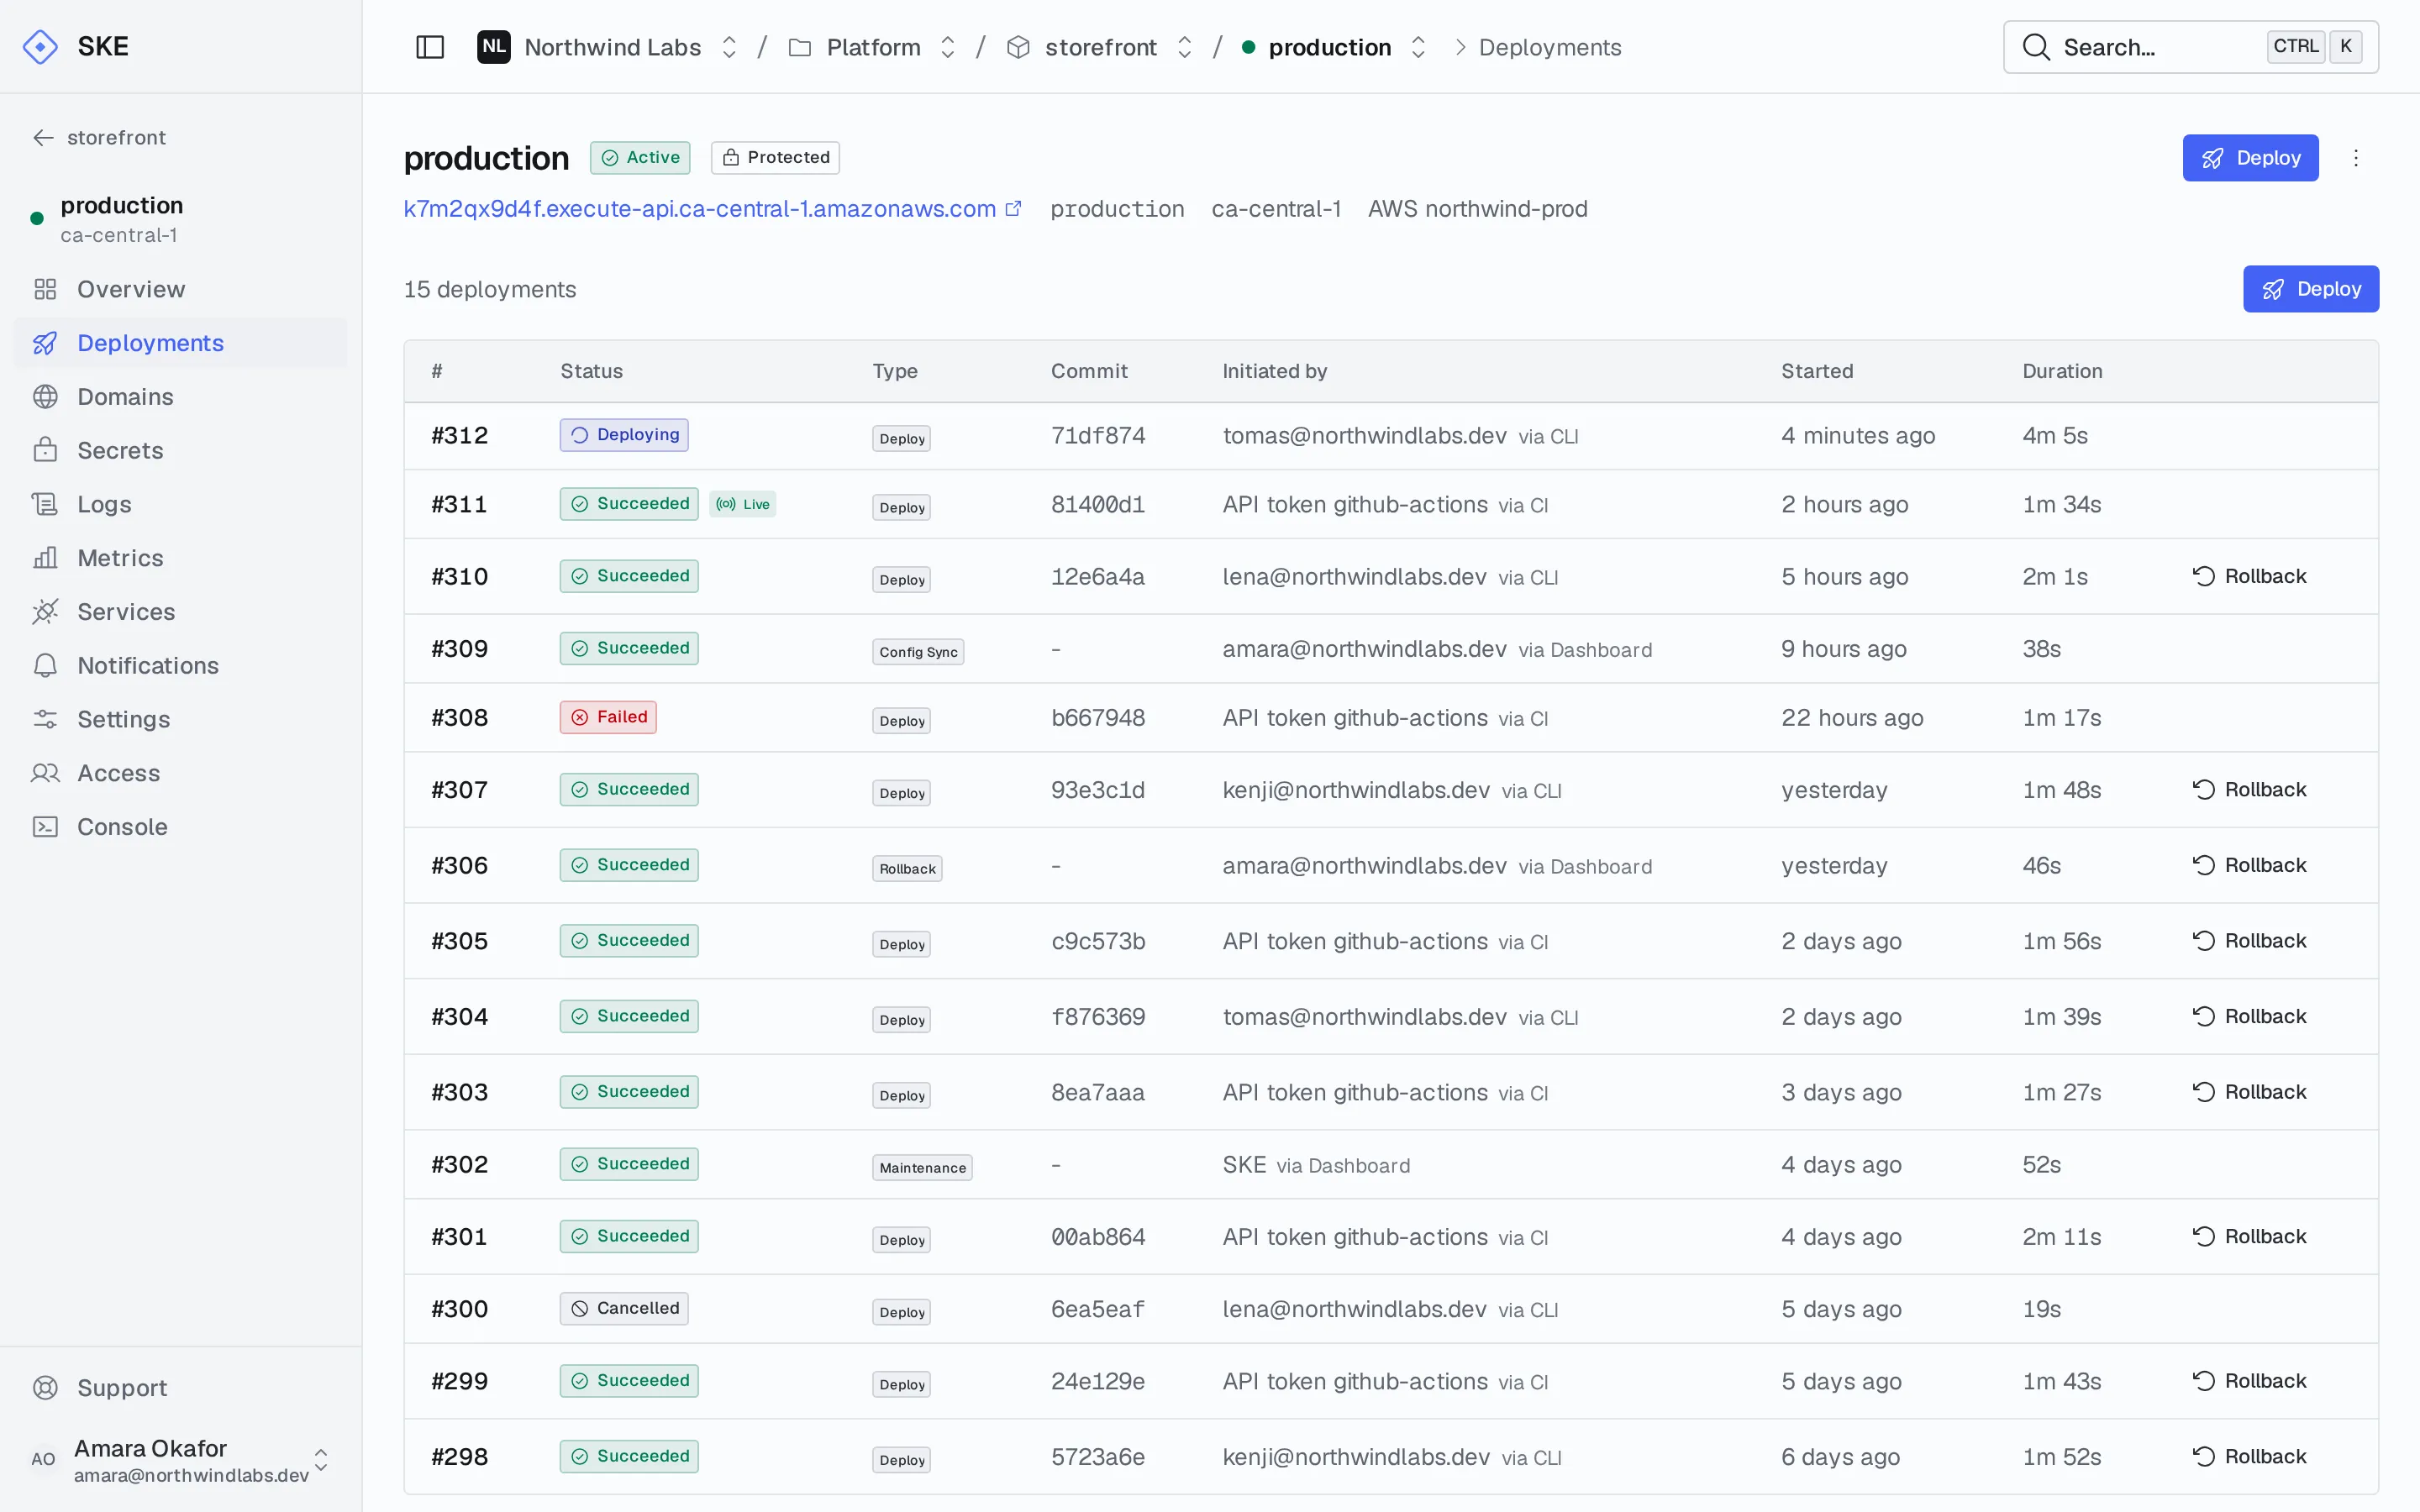
Releases are immutable images in your own registry, so every deploy is repeatable and reversible.

The production deployments list: fifteen releases with status, type, commit, who started each one from the CLI, CI or the dashboard, duration, the live release and a Rollback button on earlier ones.
One-command deploys
The CLI builds the image, pushes it to ECR or Artifact Registry, runs deploy hooks and switches traffic.
Instant rollback
Point traffic at any previous release in seconds. No rebuild, no waiting on CI.
Maintenance mode
Take an environment offline and back through a redeployment, which suits serverless compute.
Environment settings
Runtime, memory, queues, deploy hooks and domains are set per environment in the dashboard or the API, and every change is in the audit log.

Infrastructure

The services your application depends on, created in your account and sized per environment.

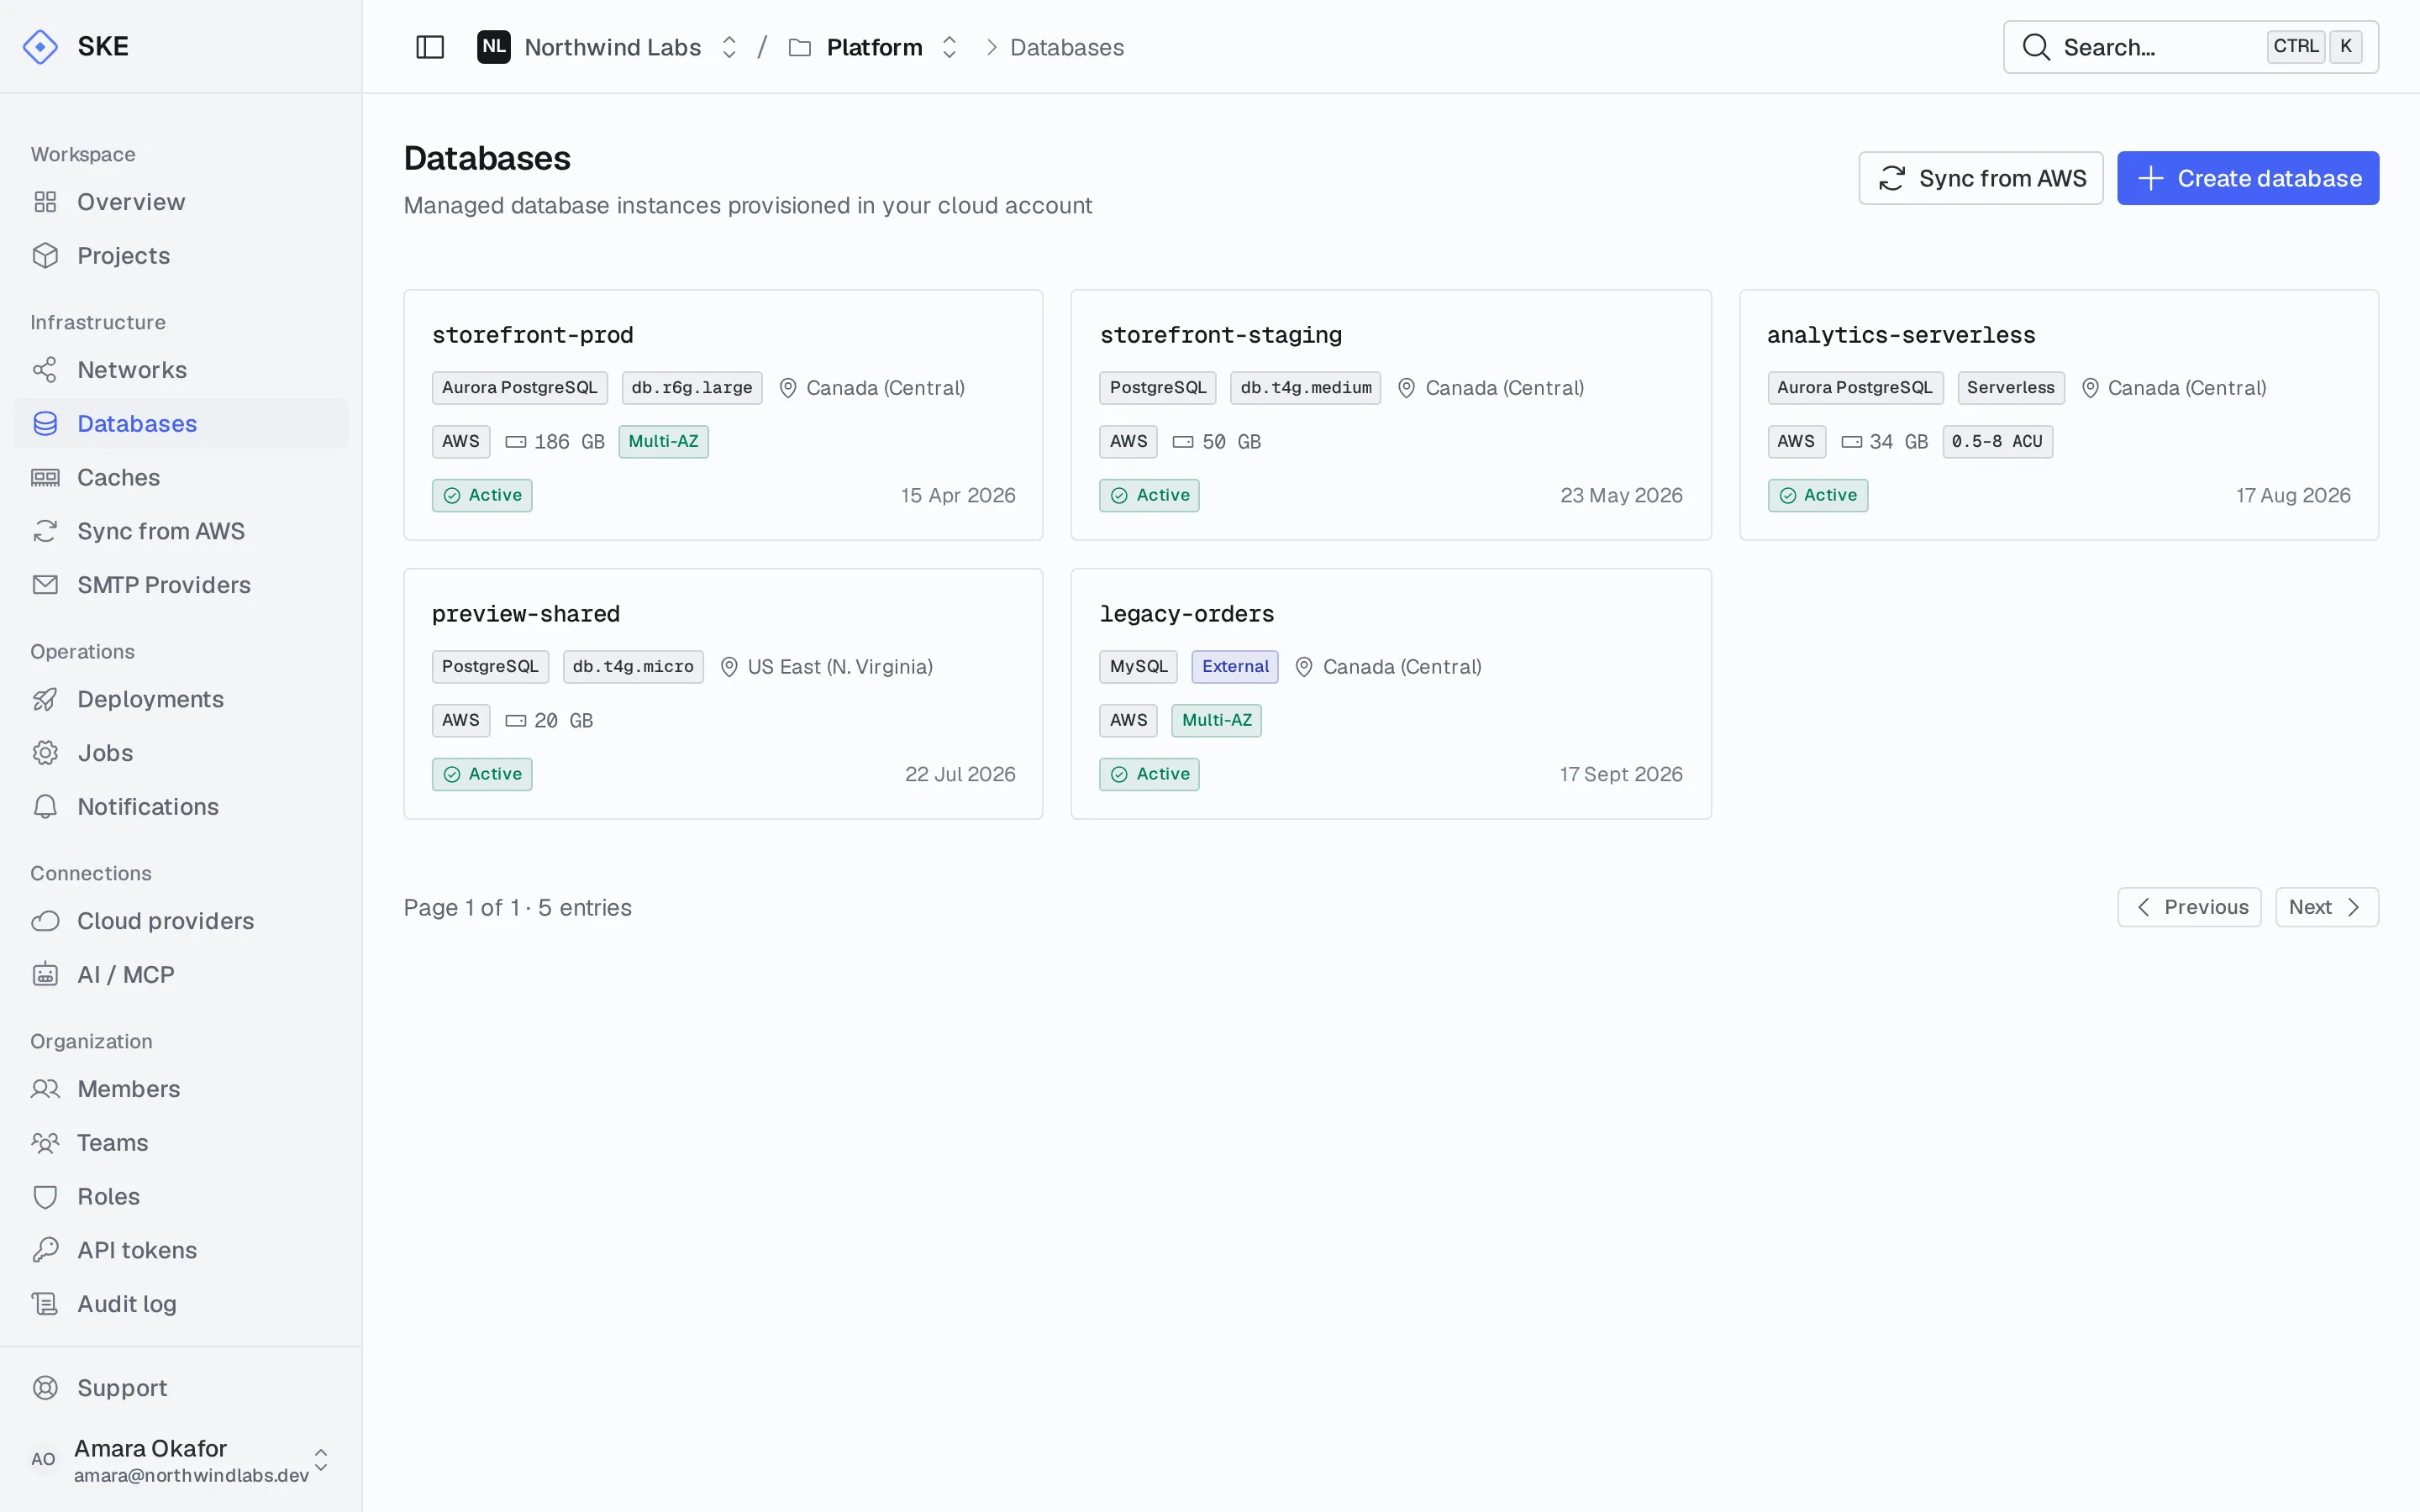
The SKE databases list: an Aurora PostgreSQL production database with Multi-AZ, a staging PostgreSQL instance, an Aurora Serverless database scaling between 0.5 and 8 ACUs, and an imported external MySQL database.
Networks
A VPC with private subnets and optional NAT, shared by the environments you attach to it.
Databases
MySQL and Postgres on RDS, Aurora or Cloud SQL, reachable only from your private network.
Caches
Redis-compatible caches on ElastiCache or Memorystore, including serverless options on AWS.
Queues and schedules
Workers on SQS or Cloud Tasks; the scheduler runs on EventBridge or Cloud Scheduler.
Custom domains
Attach your own hostnames per environment with managed TLS certificates.
Secrets
Stored in SSM Parameter Store or Secret Manager in your account and injected at startup.

Operations

Day-two tooling for running services, so on-call engineers rarely need the cloud console.

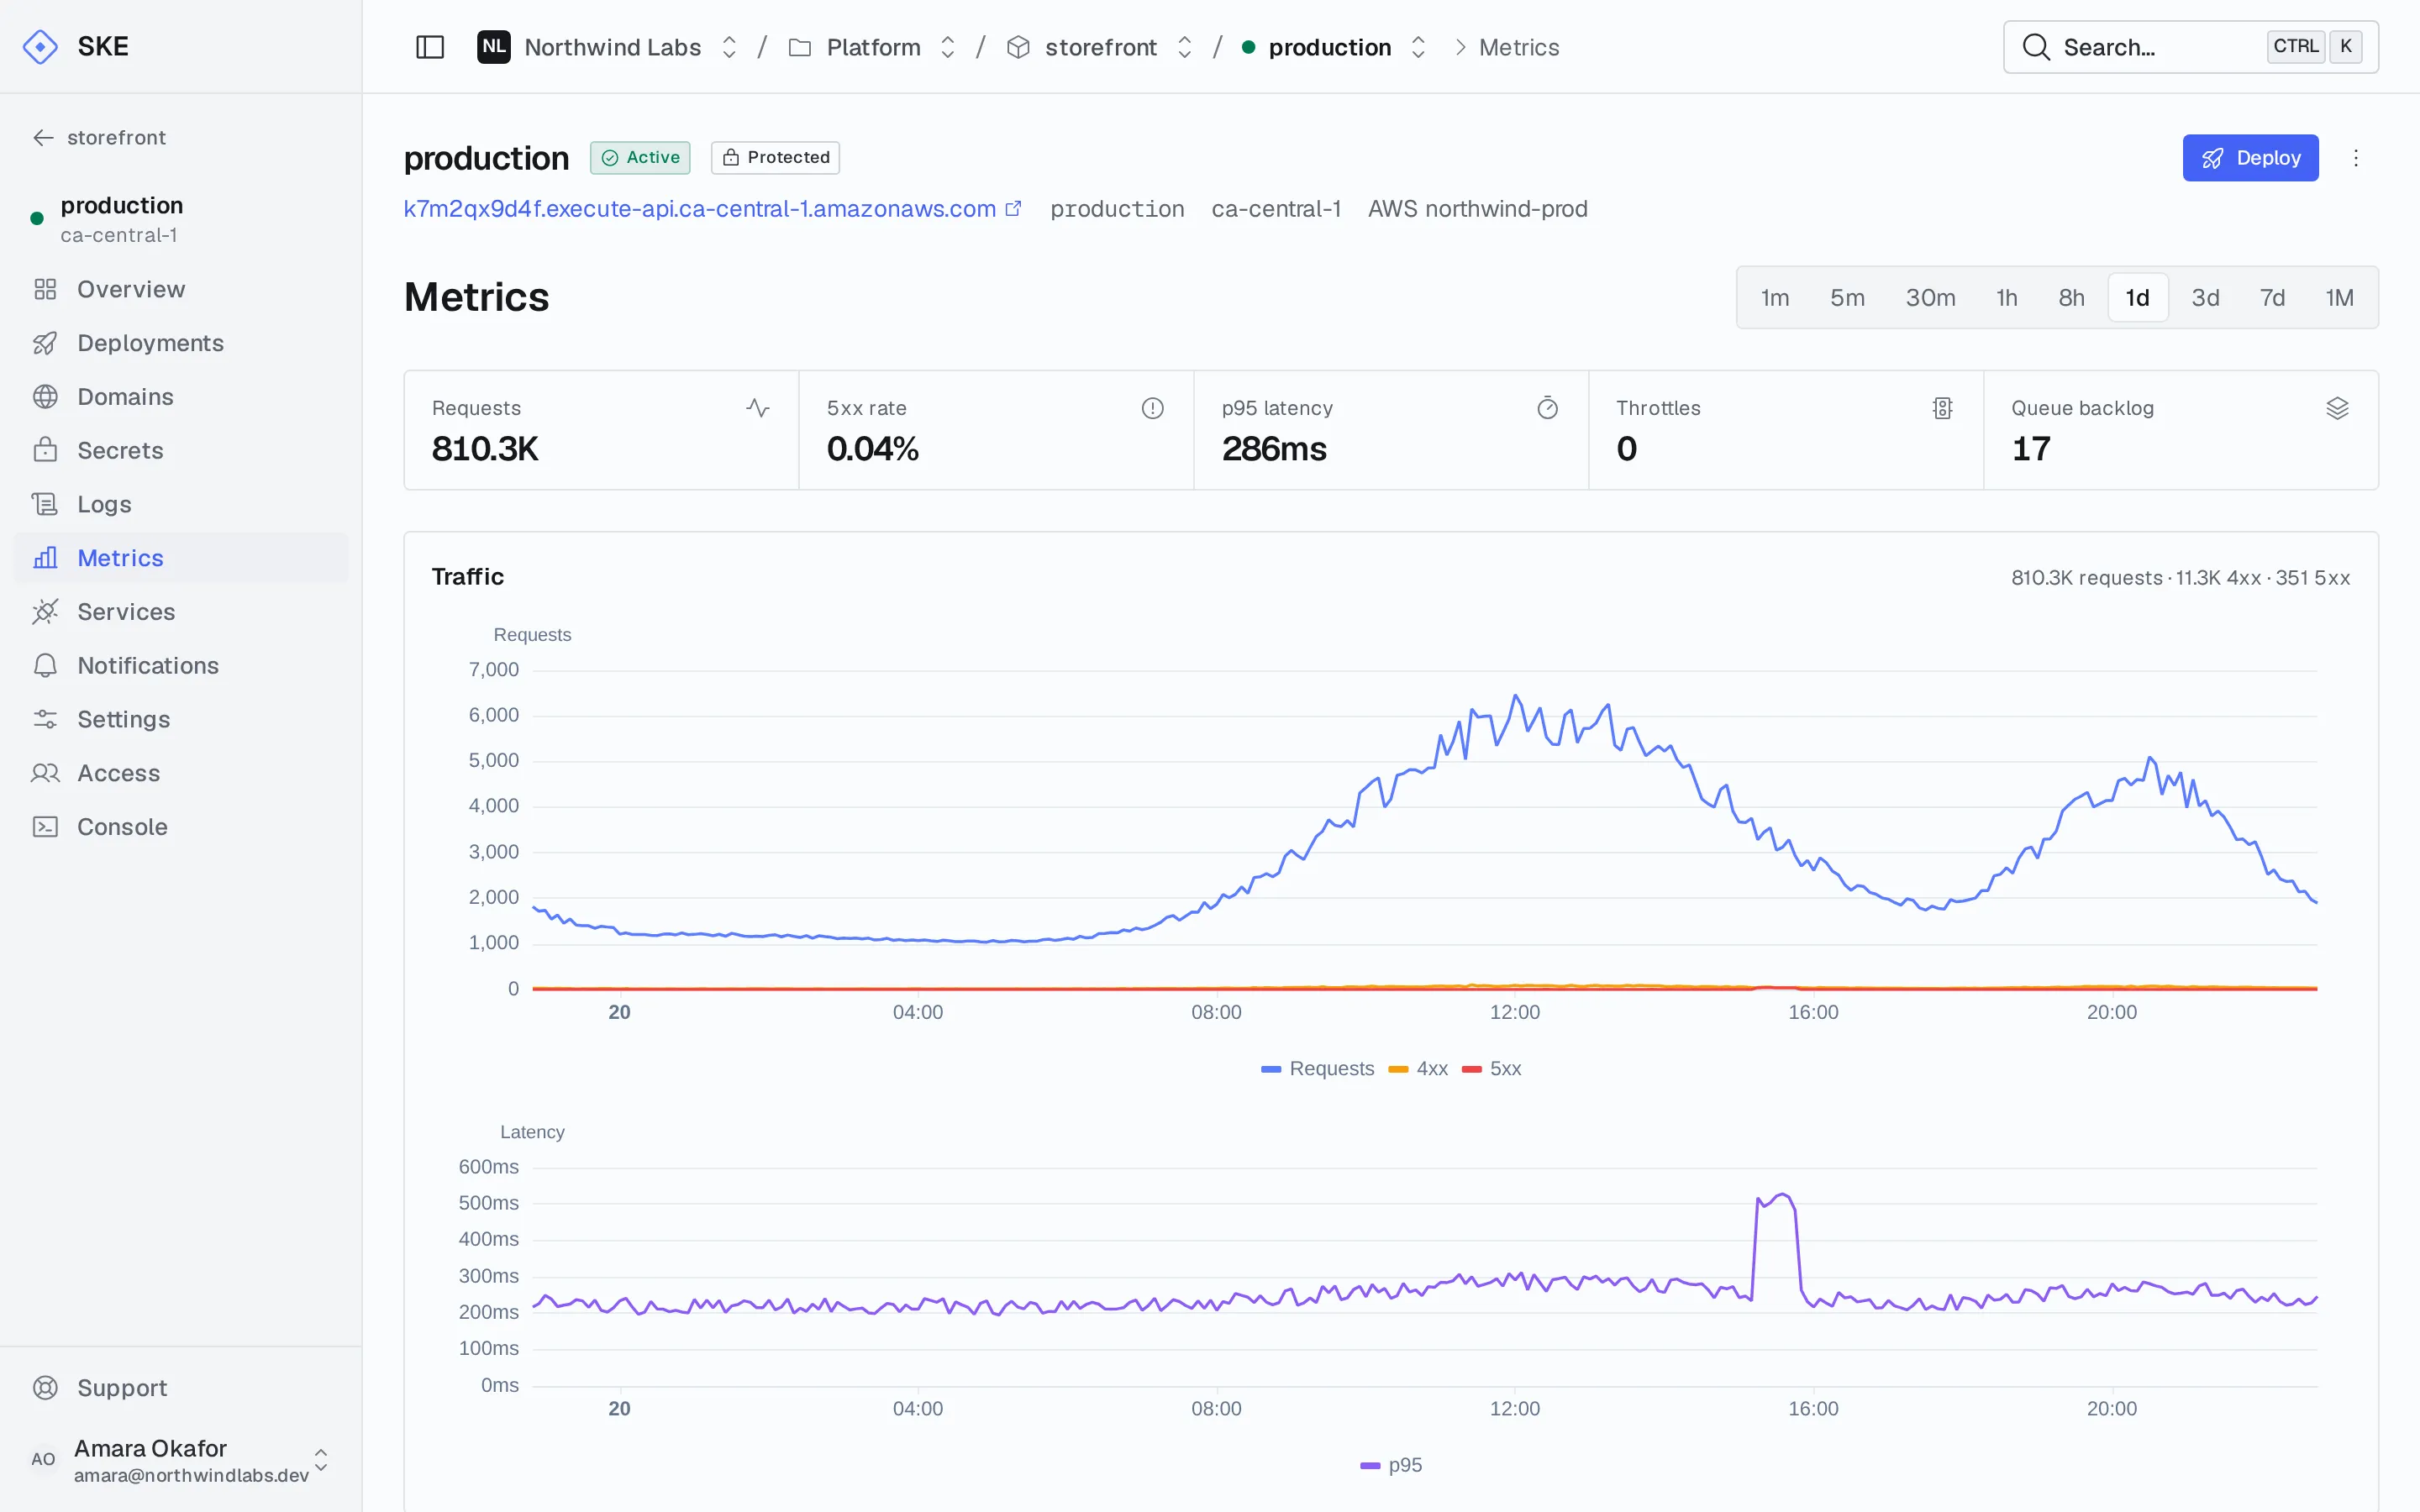
Production metrics over one day: 810.3K requests, a 0.04% 5xx rate and 286ms p95 latency, with a traffic chart peaking at midday and a latency chart with a short afternoon spike.
Logs and metrics
Search application logs and follow request, error and duration metrics per environment.
Queue control
Pause and resume individual queues during incidents or migrations.
Warmup
Pre-warm instances before a launch or a traffic spike to avoid cold starts.
Remote commands
Run one-off maintenance commands against an environment, gated by their own permission.
Diagnostics
Health checks that verify cloud access, configuration and connectivity for an environment.
Notifications
Deployment and incident alerts to Slack, Microsoft Teams, email or any webhook.

The services it uses on each cloud.

Native managed services only, so your cloud team already knows how to monitor, secure and support them.

Service AWSGoogle Cloud Google Cloud Early access
Compute and delivery
ComputeLambdaCloud Run
ImagesECRArtifact Registry
ProvisioningCloudFormation stacksGoogle Cloud APIs
Data
DatabaseRDS, AuroraCloud SQL
CacheElastiCacheMemorystore
SecretsSSM Parameter StoreSecret Manager
Operations
QueuesSQSCloud Tasks
SchedulesEventBridgeCloud Scheduler
LogsCloudWatchCloud Logging

Serverless for every team, in accounts you govern.

We are onboarding teams in small groups while SKE is in early access.